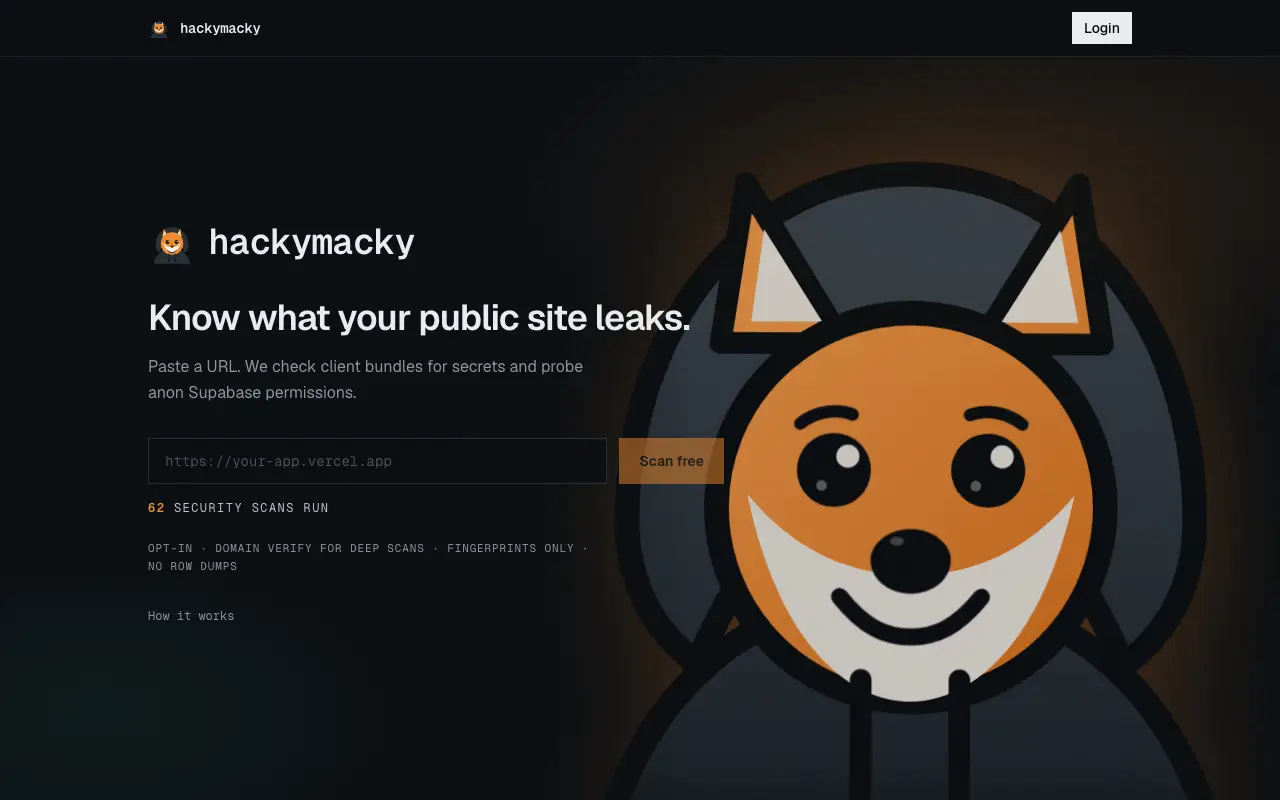
 Visit hackymacky.vercel.app ↗
What is hackymacky?
hackymacky is a security scanner designed to identify vulnerabilities in web applications built with Vercel and Supabase. Users paste a URL for a free preview scan that checks client bundles for exposed secrets and probes anonymous Supabase permissions. After domain verification, deeper scans reveal storage access, RPC capabilities, anonymous write permissions, and authentication posture, with copy-paste fixes for each finding.
The tool generates a 0–100 security score with history tracking, optional daily rescans, and integrations for GitHub Actions CI gates and Claude/Cursor via MCP. Verified projects receive email or Slack alerts on score changes. The maker built it using AI coding tools to address security gaps in Supabase row-level security policies common in AI-assisted development.
Momentum
Daily activity over the last 30 days: upvotes, unique visits, new GitHub stars and Hacker News points.
How do we know it's vibe coded?
vibetrend discovered hackymacky automatically. Evidence: HN post: "i added all the Supabase and Vercel MCPs, i expected the LLM will be a little smarter". View source.
Similar vibe-coded apps
Self-hosted Cloudflare Workers platform in a single Rust binary
AI-engineering foundation framework for building CRM/ERP and commerce apps
Multi-agent governance and collaboration platform for enterprises
Backend platform for AI agents: models, tools, database, auth, storage
Open-source platform for deploying apps via git push to GitHub
Self-hosted LINE Official Account CRM with messaging, forms, and automation