CodeDecay
Open-source PR safety checker for AI-generated code before merge
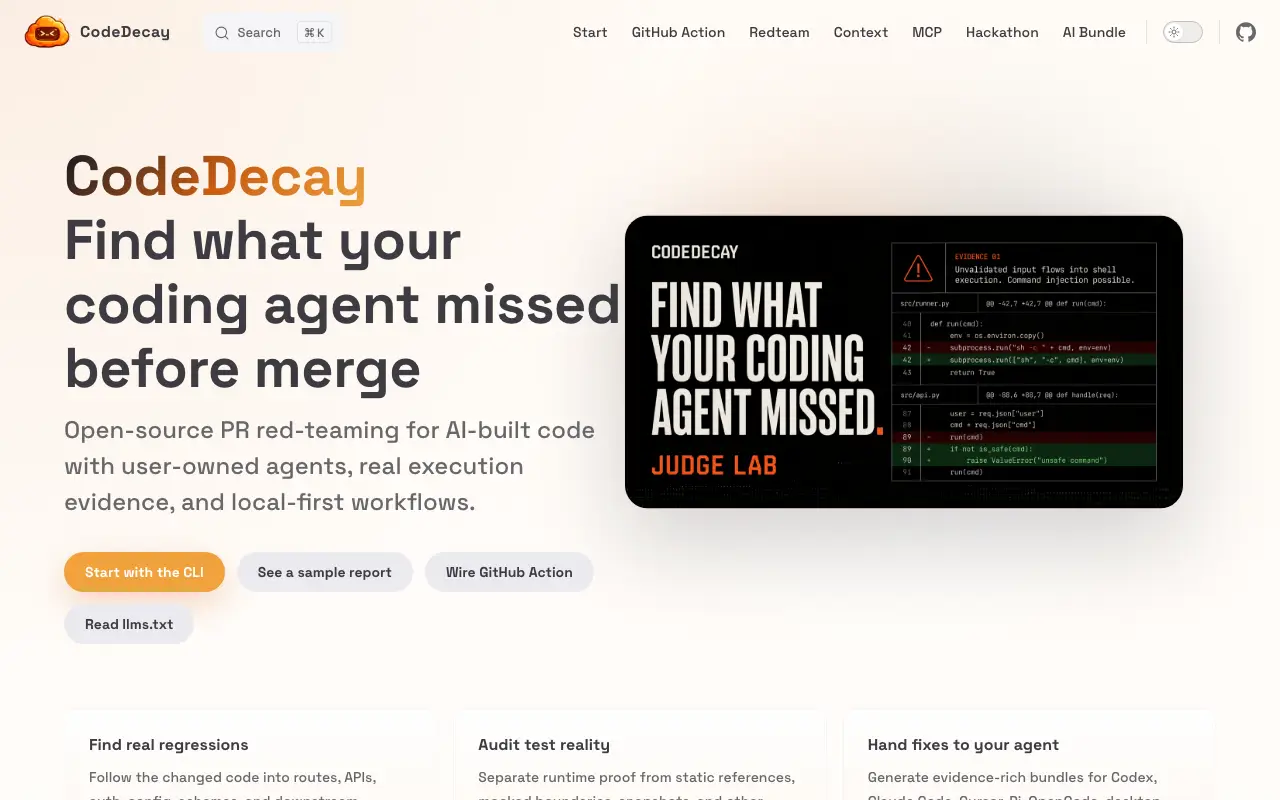 Visit submuxhq.github.io ↗
What is CodeDecay?
CodeDecay is a local-first CLI and GitHub Action that audits pull requests created by AI coding agents. It identifies weak tests, regression risks, and maintainability issues by mapping changed files to affected APIs, routes, authentication, and data schemas. The tool runs deterministic analysis without requiring cloud services or LLM calls, and generates evidence bundles for agents like Claude Code, Codex, and Cursor to fix issues in closed-loop workflows.
Designed for developers using AI coding assistants, CodeDecay separates runtime proof from static test references and mocked boundaries. It supports explicit verification through configured tests, builds, and product checks, with results surfaced as JSON and SARIF for local editors. The makers report it caught 23 of 23 planted issues in benchmarks with no false positives and zero cost.
Momentum
Daily activity over the last 30 days: upvotes, unique visits, new GitHub stars and Hacker News points.
How do we know it's vibe coded?
vibetrend discovered CodeDecay automatically. Evidence: GitHub SubmuxHQ/CodeDecay; repo has .claude, .codex, .cursor; repo topic "ai-generated-code". View source.
Similar vibe-coded apps
IDE to orchestrate multiple coding agents in one workspace
AI framework that injects project specs into coding agents across 20+ platforms
Production-grade multimodal AI model for video and audio generation
Local-first AI agent workspace with desktop GUI and terminal TUI
Prescriptive methodology and agent skills for spec-driven development with AI