mycop
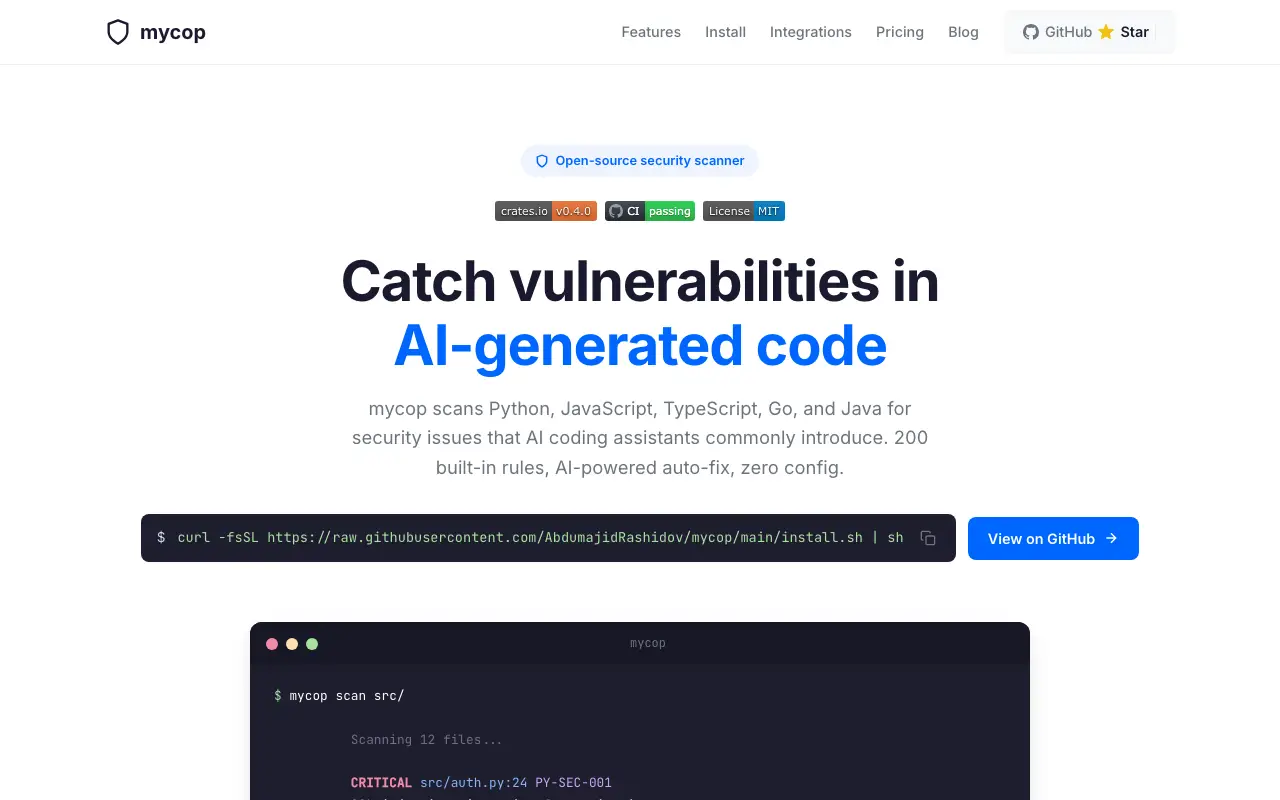
Security scanner that detects and fixes vulnerabilities in AI-generated code
 Visit abdumajidrashidov.github.io ↗
What is mycop?
mycop is an open-source static analysis tool designed to catch security flaws introduced by AI coding assistants. It scans Python, JavaScript, TypeScript, Go, and Java with 200 built-in rules covering OWASP Top 10 and CWE Top 25 vulnerabilities like SQL injection, XSS, and hardcoded secrets. The tool requires zero configuration and works offline.
Beyond detection, mycop includes AI-powered remediation that rewrites insecure code using Claude, GPT-4, Ollama, or other providers while preserving functionality. It integrates with CI/CD pipelines via SARIF output and GitHub Code Scanning, supports inline rule suppression, and offers configurable severity thresholds. The maker says it was built with Claude Code.
Momentum
Daily activity over the last 30 days: upvotes, unique visits, new GitHub stars and Hacker News points.
How do we know it's vibe coded?
vibetrend discovered mycop automatically. Evidence: GitHub AbdumajidRashidov/mycop; repo has CLAUDE.md; repo topic "ai-generated-code". View source.
Similar vibe-coded apps
 #1 this week
Open-source local voice cloning, dubbing, transcription, and audiobook creation
 #2 this week
 #5 this week
Slash commands and agents for engineers using AI without compromising standards
 #6 this week
523 free lessons building AI systems from math and first principles
 #8 this week
 #10 this week
AI-powered design intelligence toolkit for building professional interfaces
Manage teams of AI agents to run your business from one dashboard
Persistent memory for AI agents across Claude Code, Cursor, and MCP clients